Running your own AI tools? Keep them off the open internet
If your team has set up its own AI tools on a server, one report from this week deserves ten minutes. Lumen's Black Lotus Labs says a malware campaign it calls PoeLLM has infected more than 3,400 servers since at least April 2026, most of them running AI tools that anyone on the internet could reach. The Register and BleepingComputer covered it on October 7.
The headlines focus on an odd detail: the attacker hides the address of their control server inside a poem posted on GitHub. It's clever, but it isn't the part that matters for your business. What matters is how these servers were broken into in the first place.
What happened
Most victims were running open-source AI tools such as Ollama, which runs AI models on your own hardware, and LiteLLM, a "gateway" that sits between your apps and the AI models they call. Hundreds more were running Gotenberg, a PDF converter, or Gitea, a place to store code. The researchers say these were vulnerable versions, open to the internet.
Once inside, the malware uses the server's processing power to mine cryptocurrency, and uses the server to look for and break into the next one. At the peak, around 800 infected servers were active on a single day. Victims were mostly in the United States and Western Europe.
One of the flaws it uses is in LiteLLM (CVE-2026-42271). LiteLLM's advisory explains that two "test connection" features let anyone with a valid key run commands on the server, including people holding low-level staff keys. It's fixed in version 1.83.7.
Why this keeps happening
"AI makes it easier to deploy tools like LiteLLM, Ollama, or Gotenberg, but AI isn't always checking to make sure those services are patched and protected from attackers," the researchers told The Register.
That will sound familiar to anyone who has watched a pilot project grow. A self-hosted AI tool can be running in an afternoon. Someone opens it to the internet so a colleague can use it from home, and it stays that way. Nobody owns the updates. Months later it's a server nobody remembers, running old software on expensive hardware.
Exposure is usually a choice someone made. Ollama, for example, only accepts connections from the computer it's installed on until someone changes a setting. Gotenberg's own install guide warns against putting it on the internet.
Local doesn't mean private
Running AI on your own hardware can be a sensible choice. It keeps data in your hands and, for steady workloads, can make costs easier to plan. But it also means your team takes on the jobs a cloud provider would otherwise handle: updates, access, and watching who connects. When you compare local and cloud, count that upkeep, not just the hardware.
Five checks for any team running its own AI tools
1. Make a list. Write down every AI tool, model server and helper service your team has set up, where it runs and who set it up. You can't protect a server nobody remembers.
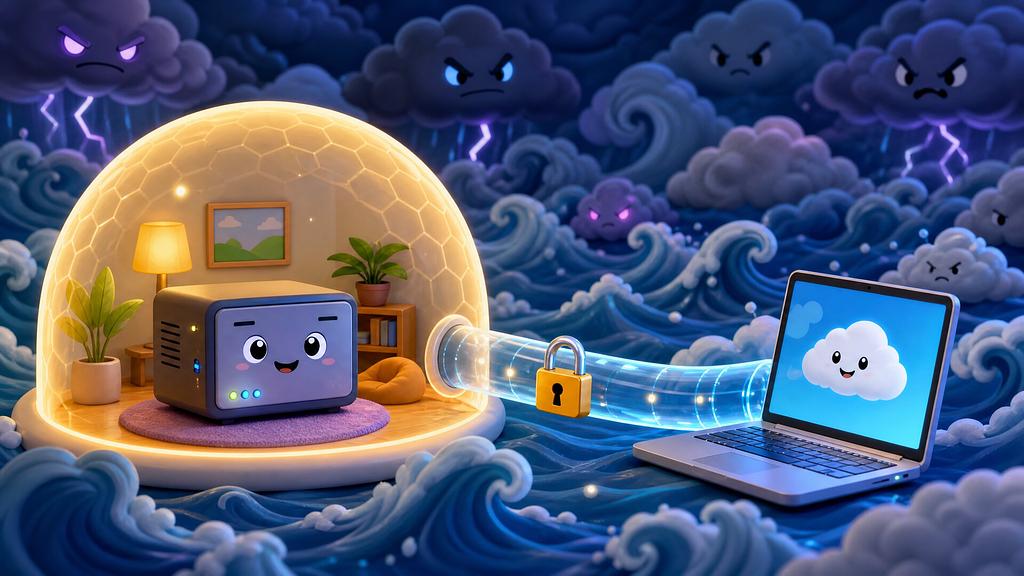
2. Keep them off the open internet. If people need access from outside the office, use a secure remote-access connection, such as a VPN, instead of opening the tool to the world, and keep that connection updated too. Lumen also recommends limiting outside access to trusted addresses.
3. Give each tool an owner. One named person checks for security updates on a regular schedule, and right away when an advisory comes out.
4. Hand out keys carefully. The LiteLLM flaw shows that even a low-level key can be a way in. Give people only the access they need, and switch off keys nobody uses.
5. Check again after every new install. Lumen advises reviewing what's reachable from outside each time a new open-source tool goes in. Ask whoever manages your network to make that part of the routine.
Where your team's tools run, and who can reach them, belongs in the plan from the start, not after the pilot.
Sources
- "Poetry is the new AI security threat as PoeLLM malware infects 3K+ servers", The Register, 2026-10-07. https://www.theregister.com/security/2026/10/07/poetry-is-the-new-ai-security-threat-as-poellm-malware-infects-3k-servers/5301672
- "PoeLLM malware infects exposed AI servers in cryptomining attacks", BleepingComputer, 2026-10-07. https://www.bleepingcomputer.com/news/security/poellm-malware-infects-exposed-ai-servers-in-cryptomining-attacks/
- "Canto incognito: tracking the PoeLLM malware", Lumen Black Lotus Labs, 2026-10-07. https://www.lumen.com/blog/en-us/canto-incognito-tracking-the-poellm-malware
- "LiteLLM: Authenticated command execution via MCP stdio test endpoints" (CVE-2026-42271, GHSA-v4p8-mg3p-g94g), GitHub Advisory Database / BerriAI, published 2026-04-21, updated 2026-06-09. https://github.com/advisories/GHSA-v4p8-mg3p-g94g
- "FAQ", Ollama documentation, accessed 2026-10-08. https://docs.ollama.com/faq
